
Integration Notes
Server-To-Server integration
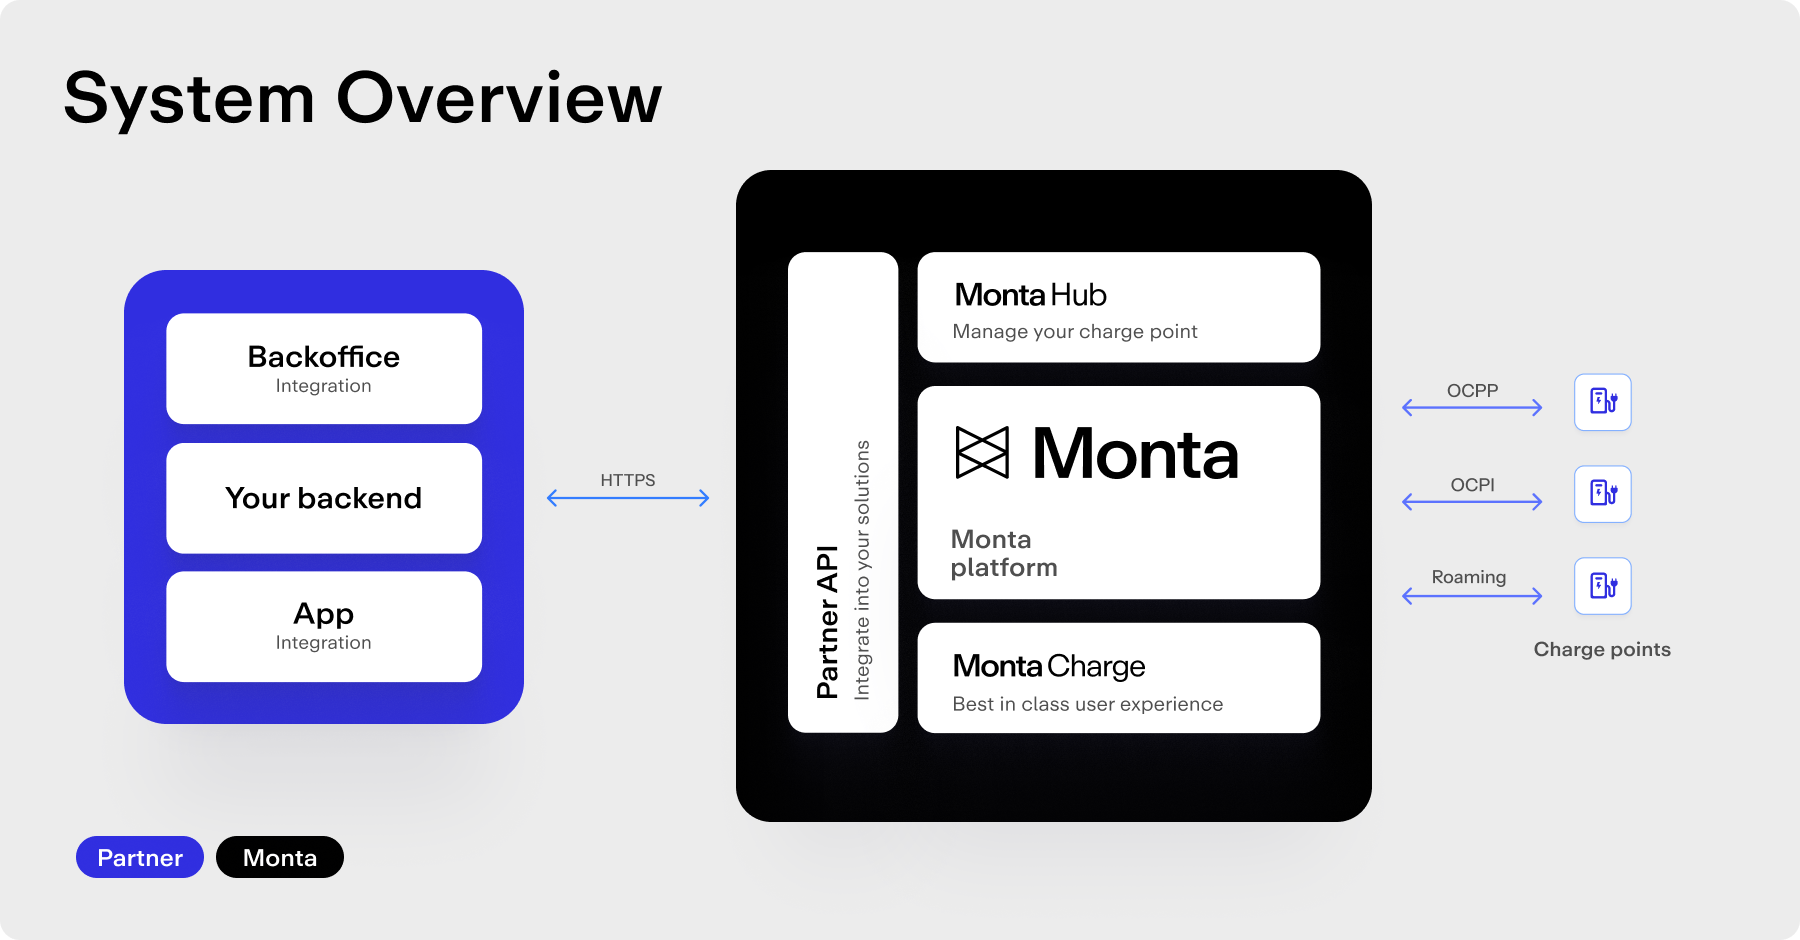
We expect a server-to-server integration; your clientId and clientSecret should not be part of any frontend (app, web, …).
Rate Limiting
Quota-based Policy
Our APIs are rate-limited. Rate-limits can be configured for each client credential. After you have obtained an accessToken, you can use the [/auth/me](/api/authentication#obtain-information-about-current-api-consumer) endpoint to see your rate limit. It's determined by two fields:
rateLimit, e.g. 1000rateLimitIntervalInSeconds, e.g. 600
This means that you can perform 1000 calls to our API within 600 seconds (10 minutes) before you get rate-limited (until the next 600s block starts).
Response headers (example):
Code
In case you exceed the rate limit, our API will return with status code 429 (Too Many Requests).
Default Rate Limit
The default rate limit, unless agreed otherwise, is 1000 requests per 10 minutes for our Enterprise partners.
Fair-Use Policy
Some endpoints might not be rate-limited. For these the Fair Use Policy applies.
Response headers (example):
Code
Pagination
All endpoints that return a collection are paginated using Offset Pagination.